Cyber regulatory compliance you can prove.
DICB trains professionals to interpret regulatory requirements, translate them into accountable obligations, determine what evidence should exist, and make assurance judgements they can defend.
Regulation, translated into obligations you can run.
One repeatable method takes any cyber regulation from open-textured legal text to system-level controls, named owners and a record another professional can test and maintain.
Not what the policy says. What you can prove happened.
Evidence assessed against the claim it supports, tested for provenance, and honest about when it has gone stale. The standard a board, an auditor or a regulator will hold you to.
Governance
Who owns the decision, under what authority, and what the record shows.
Regulation
What the law requires today, what is draft, what is proposed, and the difference.
Evidence
What an organisation can actually demonstrate, to a board, an auditor or a regulator.
The gap between knowing what a regulation says and being able to show how you comply
Regulated organisations have frameworks, tooling and growing supervisory pressure, and still cannot answer the simple questions: which systems carry this obligation, who accepted this risk, and what evidence proves the control worked last week.
DICB is not a beginner cybersecurity bootcamp. It develops the people who will be asked to sign, approve or defend: the ones who must turn regulatory language into obligations an organisation can run, prove and keep current as systems, people and requirements change.
Five seats at the table. One question each.
DICB is built for the people who will be asked to sign, approve or defend. Each of them hears the same kind of question, and each leaves with a way to answer it.
Boards and executives
Did you know this was running, and who approved it?
A one-page briefing format and the five questions to ask before signing anything.
Risk, compliance and audit
Show me the evidence that this control operated last quarter.
A register entry, a claim-relative evidence test, and an honest residual rating.
Legal and data protection
Is this an automated decision under section 35, and did we assess it?
A legal screen that separates what binds today from what is draft or proposed.
Technology and security
What does the supplier actually retain, and can you prove it?
Controls matched to failure modes, with the design evidence and the operating evidence kept apart.
Consultants and advisers
Which method did you use, and would another professional reach the same answer?
One published, examinable method to bring to every client.
Nairobi, 31 October 2026
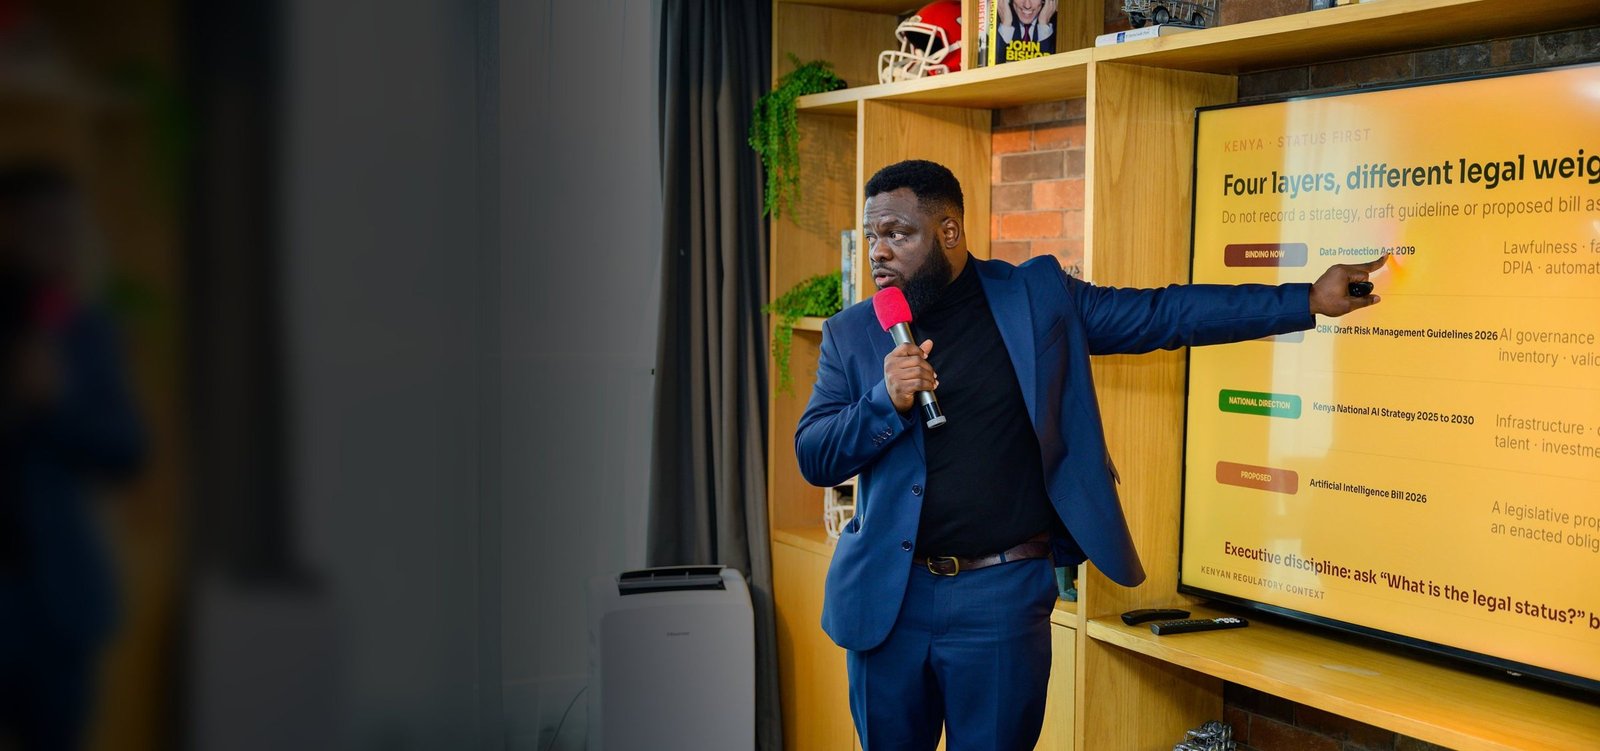
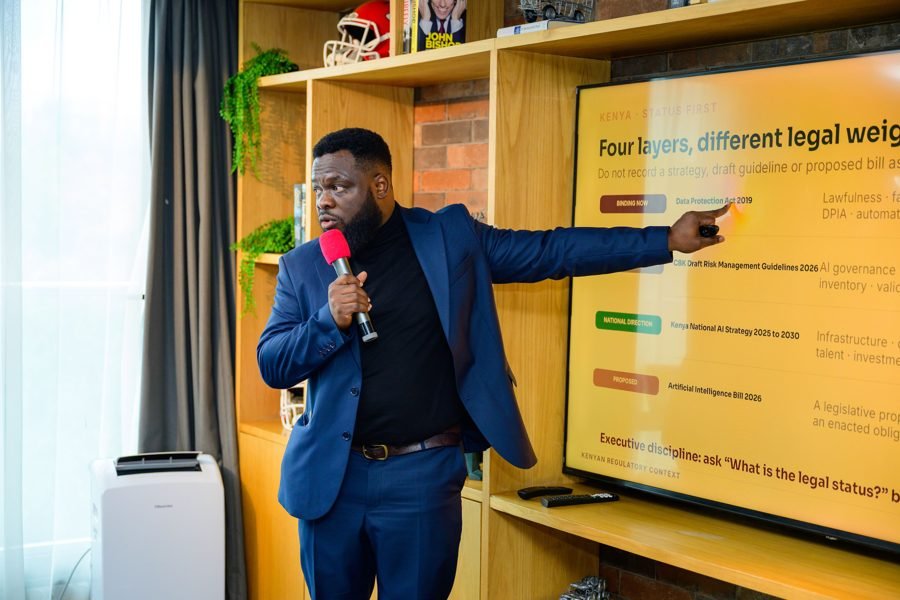
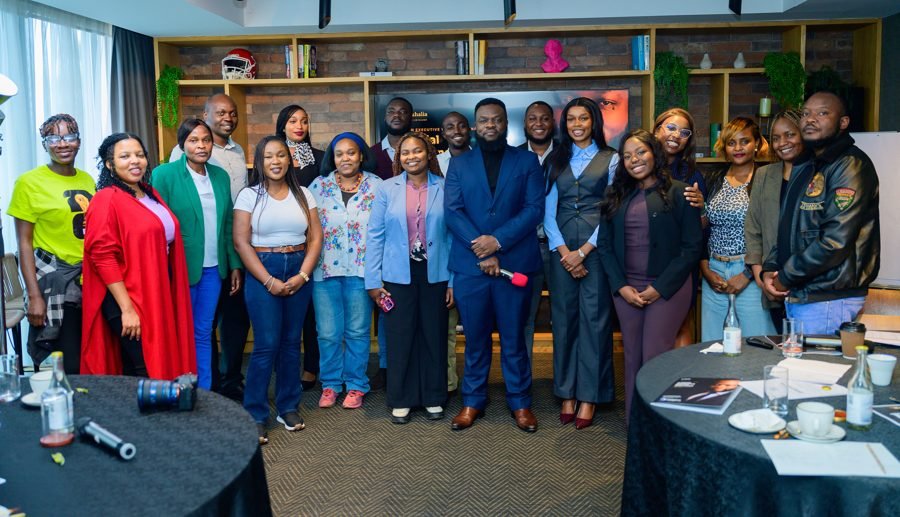
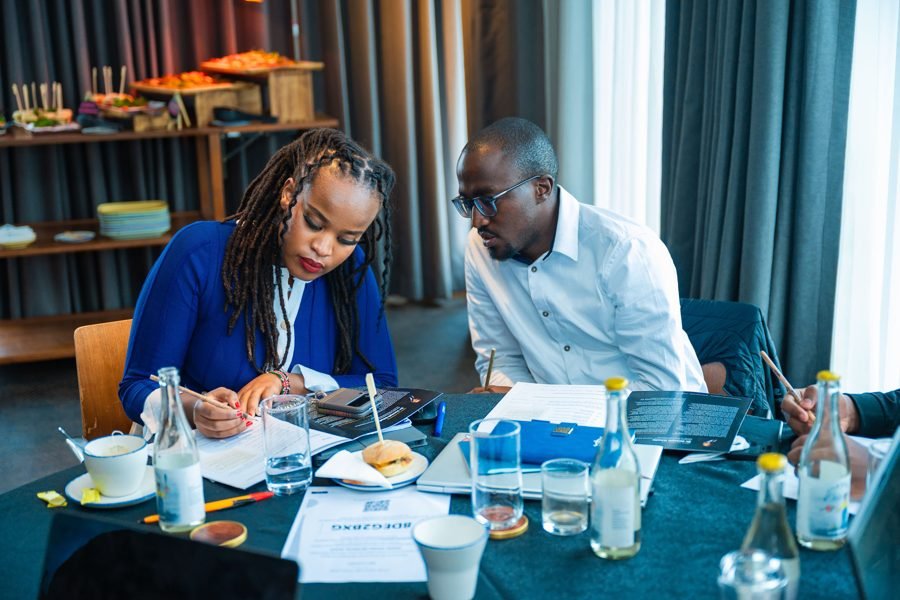
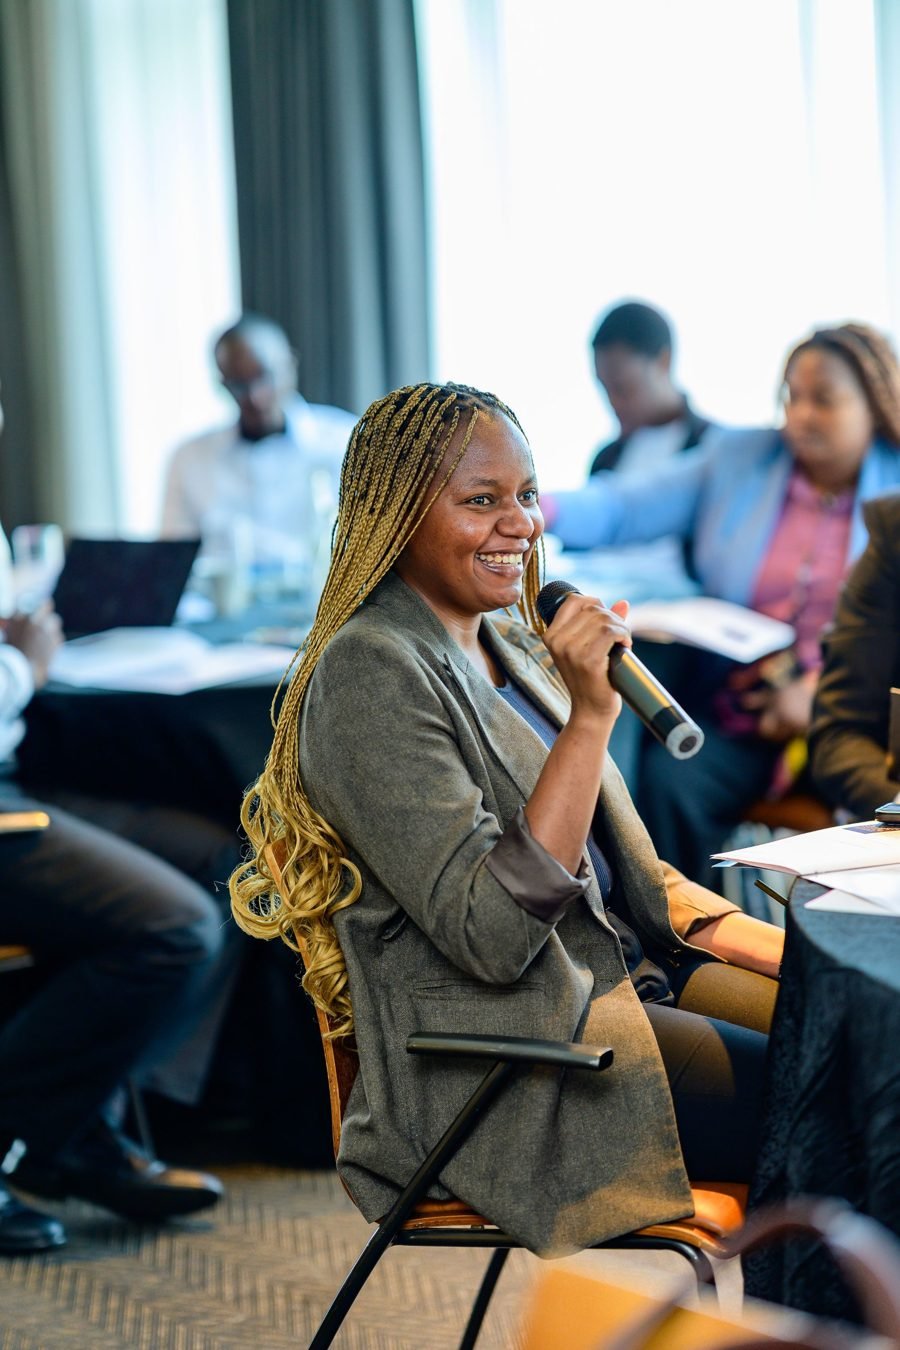
DICB’s first executive workshop in Kenya, Artificial Intelligence Risk and Governance: From Policy to Evidence, sold out at The Social House Nairobi, in partnership with RisqPro Group. Thirty professionals from banking, law, technology, insurance and government assessed a real use case, built a risk register entry, screened it against Kenyan law and wrote a one-page briefing their leadership could act on.


DICB Certified Cyber Regulatory Practitioner
Complete the course, pass the examination, become certified.
A self-paced course of about five hours, with a workbook, teaching one reliable method for taking any cyber regulation and turning it into something an organisation can run, prove and defend. You work on a real regulation of your choice and build the compliance record yourself, module by module.
The DICB-CCRP is the examined professional designation for practitioners who can apply the method. Launching December 2026.


Train your people. Build your governance. Keep it current.
Executive briefings, private cohorts and bespoke workshops. Cyber regulatory compliance services and artificial intelligence use case assessments built on the DICB method. Retained advisory for the questions that arrive between projects.
Legal review through our advocate partners. DICB does not certify governance it built; independence is part of the method.
A control is not what the policy says should happen. It is what you can prove happened.Dr Joseph Ikhalia, Nairobi, 31 October 2026
Published, and open to challenge
DICB’s method rests on The Three Problems of Cyber Regulatory Compliance: Translation, Institutional Continuity, and Evidence Quality, a position paper by Dr Joseph Ikhalia published on SSRN in July 2026, and on the Institutional Cyber Judgement Doctrine. The problem analysis is published so that it can be tested separately from the DICB codification that answers it.